SonicWall Gen 6 Firewalls Reach End of Security Patches
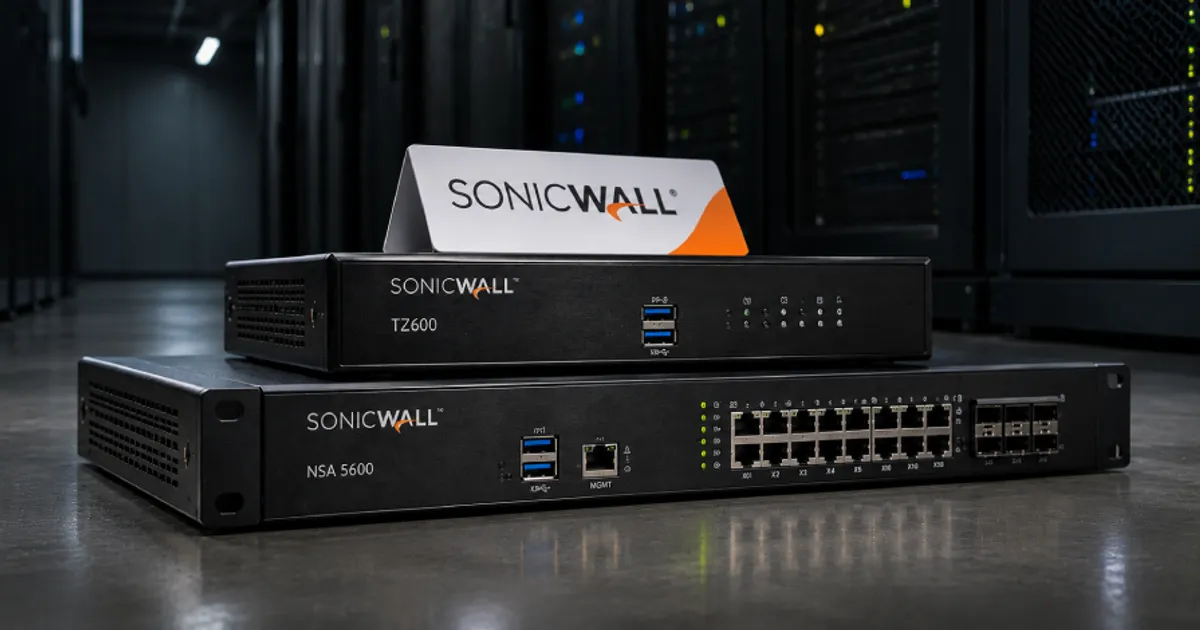
SonicWall urges customers to retire Gen 6 firewalls running SonicOS 6.x, which will get no more security fixes even for critical flaws, and move to Gen 8 with SonicOS 8.
⚡ Why it matters
Unsupported edge devices are prime initial-access targets; any new flaw in an internet-facing Gen 6 unit will stay open permanently.
SonicWall has warned customers that its Generation 6 firewalls running SonicOS 6.x no longer receive security updates, including for critical vulnerabilities, and should be retired and replaced.
The vendor expects internet-facing Gen 6 devices to be actively targeted, pointing out that adversaries now lean on automated tooling and AI to locate and compromise out-of-support perimeter hardware quickly.
Affected models
The list covers TZ models (TZ300 through TZ600 and wireless variants), SOHO and SOHO 250, the NSA 2600–6600 and NSa 2650–9650 series, NSv 10 to NSv 1600 virtual appliances, SuperMassive 9200–9800, and NSsp 12400 and 12800.
Context
Google Mandiant's M-Trends 2026 report estimated that the mean time to exploit has turned negative, at about seven days before a patch is available, and VPNs and firewalls feature heavily in CISA's KEV catalog.
Recommendations
- Inventory every Gen 6 firewall and retire it, starting with internet-exposed and remote-access units.
- Migrate to a Gen 8 firewall running SonicOS 8 with an authorized partner.
- Until replacement, disable WAN management (HTTPS, SSH, SNMP) and disable SSL VPN or restrict it to known addresses.
- Enforce MFA on all admin and remote-access accounts and reset local passwords.
- Disable unused services and watch logs for unusual logins and configuration changes.
🔗 Sources
This article is original reporting by the Security World editorial team based on the sources listed above; direct quotes are kept short and marked with quotation marks. Corrections and feedback: info [at] securitywd.net.
Related stories
Cisco Expressway CVE-2026-76466 Exploited After PoC Release
F6 says attackers abused CVE-2026-76466 in clustered Cisco Expressway devices to gain root and stage lateral movement at a Russian organization. Fixed in X15.5.20.
CISA KEV Adds Exploited LiteLLM, REDCap, Apache Axis and Synology Flaws
CISA added four actively exploited vulnerabilities to its KEV catalog, affecting BerriAI LiteLLM, Vanderbilt REDCap, Apache Axis and Synology, with federal deadlines of Nov 21 and Dec 2.
PHP Security Releases Due Nov 19 Fix Critical Flaws, Incl. CVE-2026-115560
PHP will ship security releases on November 19, 2026 for all supported branches, with the top severity rated critical. CVE-2026-115560, a conditional RCE, is expected to be included.